 Arrow
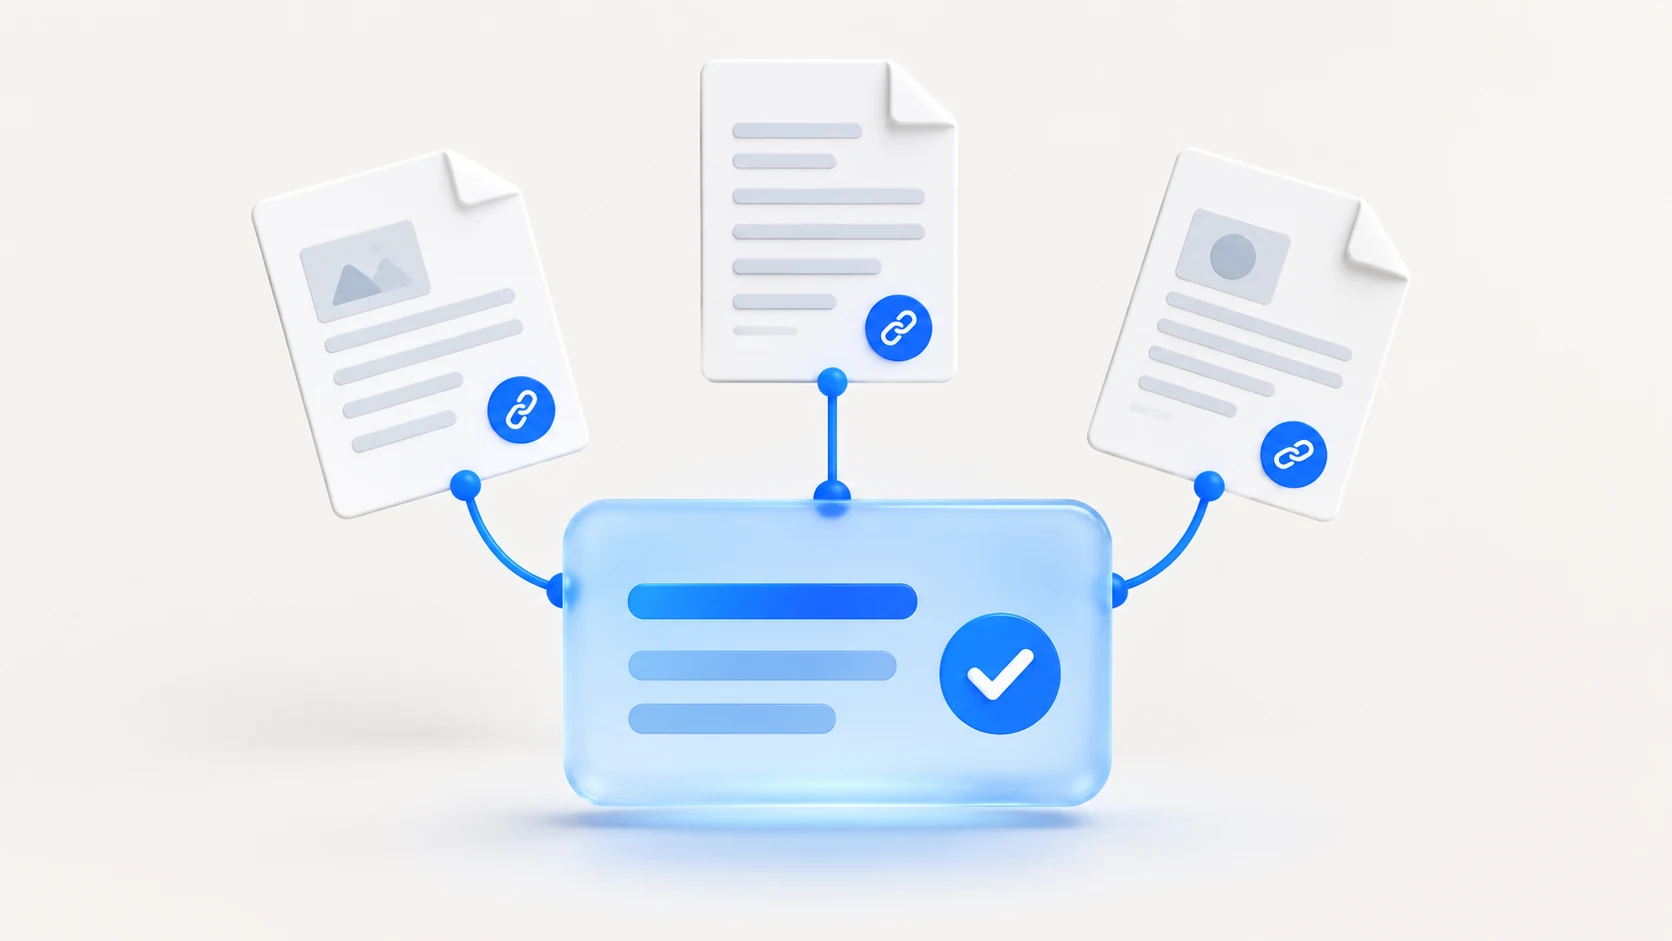
Show an authorized sample report structure, methodology, reviewer roles and the process for validating findings. Explain how severity and remediation recommendations are documented. A redacted example can demonstrate report quality without disclosing exploitable customer details or implying that a sample finding describes every environment.
Demonstrate the deliverable safely
Describe the executive summary, technical evidence, limitations and retest scope. Make clear which sample sections are illustrative. Verify any credential references against their exact holder and scope, and avoid presenting a report template as a measured customer security outcome.
Keep the sector facts verifiable
A technical owner should review test scope, deliverable descriptions and public security claims. Distinguish an authorized assessment from continuous protection or incident response. Publish sanitized sample material only after review; credentials, vulnerabilities and customer infrastructure details require an appropriate private channel.
What to check
- Review samples for confidential technical details.
- Explain evidence and finding validation.
- Distinguish a sample report from a client result.
A practical example
A sample report page shows a sanitized finding format and explains how the team records evidence and remediation verification, while omitting real targets and access details.
Sources and further reading
These steps are Arrow AI's implementation guidance. The example is illustrative; it is not a measured customer result. Publication and source access do not guarantee an AI recommendation.
Apply this to your website
Identify the source gaps and decide what to improve with Arrow's free audit. Review what Arrow GEO measures before choosing a reporting scope.